🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction
Preview text: 🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction 96 ⚠️…
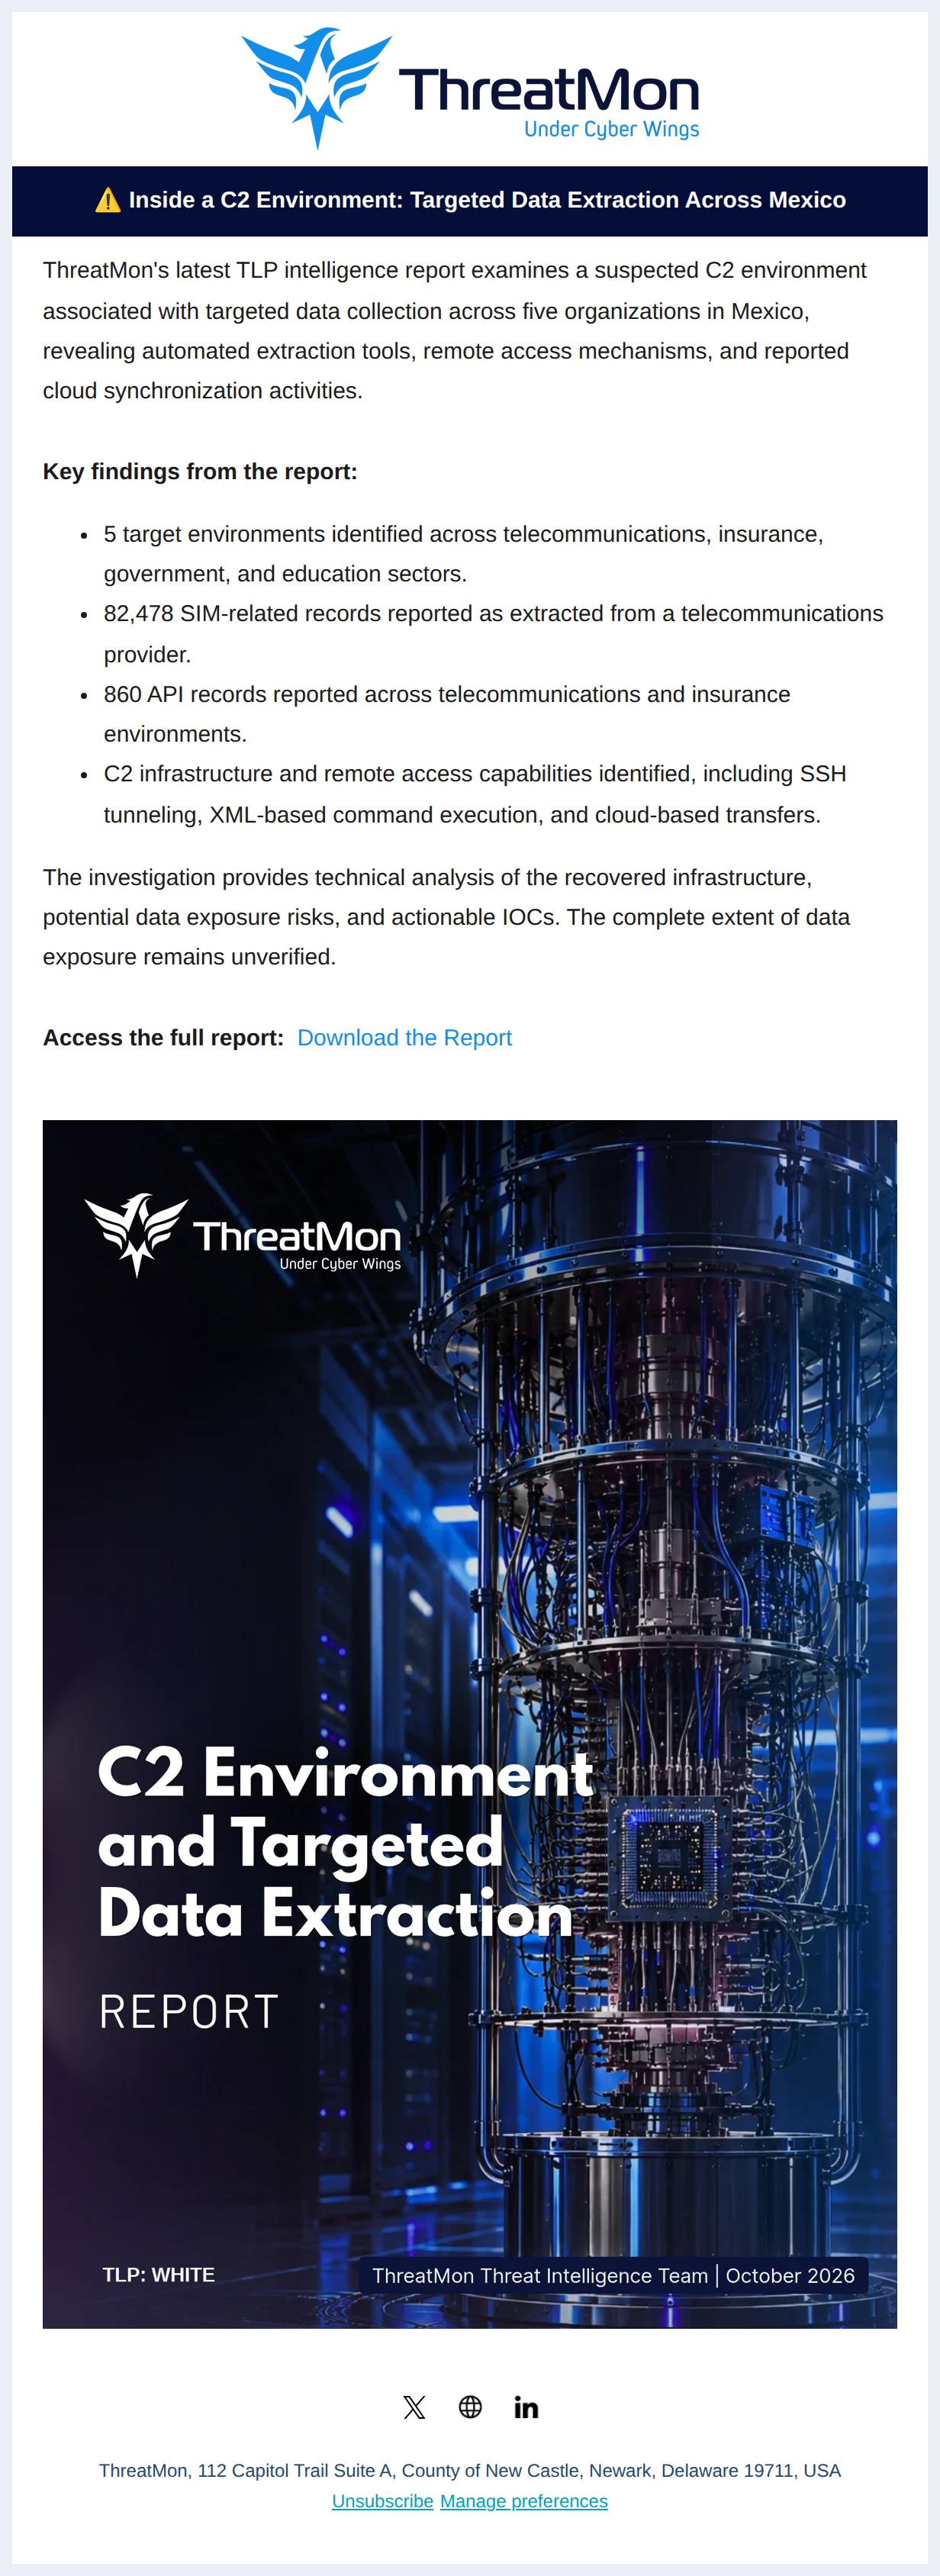
Using this email in an article? Credit: ThreatMon Research email via They Sent It, with a link to this page. Full-size image
- Subject
- 🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction
- Preview text
- 🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction 96 ⚠️…
- From
- research@
threatmonit.io - Brand
- ThreatMon Research
- ESP
- HubSpot
- Sent
- Sat Oct 31, 2026, 10:37 AM ET
- Sent to
- shadowid.io, threatflood.io, threatmon.io, threatmonit.io
- Size
- 39 KB
- Images
- 6
- Links
- 6, 2 of them buttons
- Subject length
- 77 characters
Against ThreatMon Research's usual
Sent in the 10 AM hour, which holds 6% of its emails; 19% arrive in the 7 AM hour. The subject is 77 characters; its average is 58.
Email headers
What the brand's servers put on this email. Our receiving servers, the address we subscribed with and unsubscribe links are left out.
- From
- ThreatMon Research <[email protected]>
- Reply-To
- [email protected]
- Subject
- 🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction
- Date
- Sat, 31 Oct 2026 10:37:08 -0400
- Message-ID domain
- bf05x.hubspotemail.net
- Return-Path domain
- bf05x.hubspotemail.net
- DKIM signature
- d=bf05x.hubspotemail.net s=hs2; d=threatmonit.io s=hs1-45734016
- Authentication
- dkim=pass (bf05x.hubspotemail.net), dkim=pass (threatmonit.io), spf=pass (bf05x.hubspotemail.net), dmarc=pass (threatmonit.io)
- List-Unsubscribe
- Present, one-click
- Feedback-ID sender
- HubSpot
Servers it passed through, newest first
- from bid47uj.bf05x.hubspotemail.net [158.247.24.105] by our receiving server with ESMTPS
Other sending headers (names only): X-HS-Cid, X-Report-Abuse-To
Sent just before and after
| Nov 4, 2026 9:06 AM | 🚨New ThreatMon Report | October 2026 Ransomware Landscape | |
| Nov 3, 2026 1:01 PM | 🚨New ThreatMon Research | The Fake Zero-Day Trap | |
| Oct 31, 2026 10:37 AM | 🚨 ThreatMon Intelligence Report | C2 Environment and Targeted Data Extraction (this email) | |
| Oct 23, 2026 5:23 PM | 🚨 New ThreatMon Research | From Underground Forums to SOC: PHP2Shell | |
| Oct 23, 2026 1:50 PM | 🚨New ThreatMon Research | Ransomware Threat Landscape in Türkiye | |
| Oct 22, 2026 7:29 AM | New ThreatMon Research | Mosad Threat Actor Analysis | |
| Oct 16, 2026 6:05 AM | ThreatMon’s October 2026 Product Updates |
More from ThreatMon Research
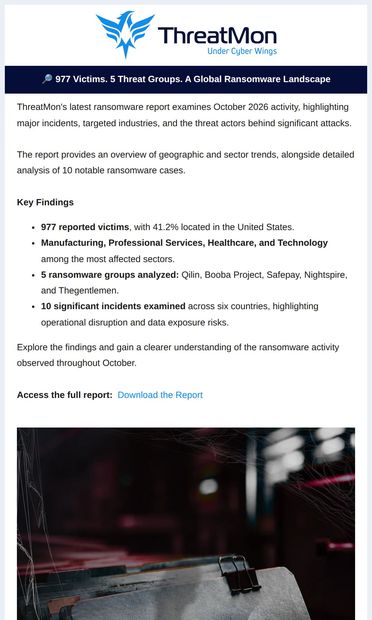
All ThreatMon Research emails🚨New ThreatMon Report | October 2026 Ransomware Landscape
Nov 4, 2026 9:06 AM
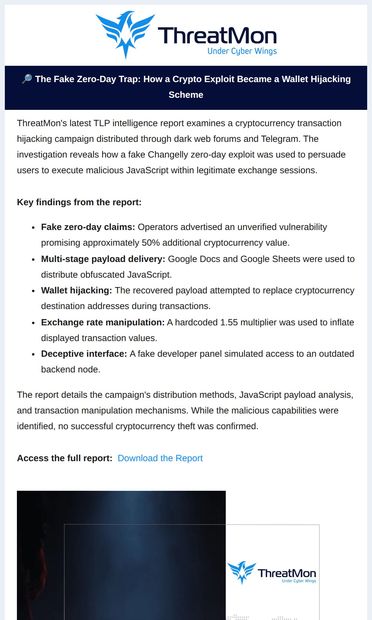
🚨New ThreatMon Research | The Fake Zero-Day Trap
Nov 3, 2026 1:01 PM
🚨 New ThreatMon Research | From Underground Forums to SOC: PHP2Shell
Oct 23, 2026 5:23 PM
🚨New ThreatMon Research | Ransomware Threat Landscape in Türkiye
Oct 23, 2026 1:50 PM
New ThreatMon Research | Mosad Threat Actor Analysis
Oct 22, 2026 7:29 AM
ThreatMon’s October 2026 Product Updates
Oct 16, 2026 6:05 AM
New ThreatMon Research | ASTRO C2 Technical Analysis
Oct 15, 2026 7:32 AM
🚨 New Threat Report Published : Ransomware 2026 Report September
Oct 8, 2026 9:03 AM
Sent the same day by similar brands
Same ESP and the closest weekly volume, sent on Oct 31, 2026.